Strengthen Your Cyber Defenses: Discover the Power of VAPT!
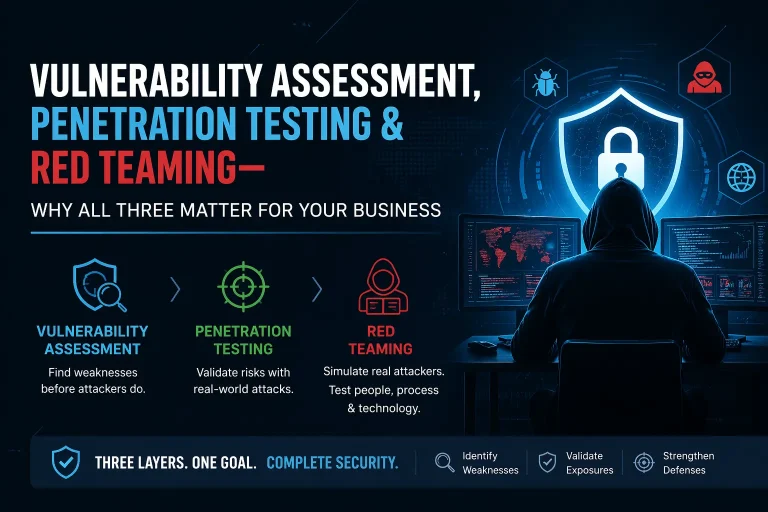
Vulnerability Assessment and Penetration Testing (VAPT) is a comprehensive approach to identifying, assessing, and mitigating security vulnerabilities in an organization’s IT infrastructure. It combines two essential security activities:
- Vulnerability Assessment (VA): This process involves systematically scanning and identifying security weaknesses in systems, applications, and networks. The goal is to detect known vulnerabilities and potential security gaps that could be exploited by attackers.
- Penetration Testing (PT): Also known as ethical hacking, this process simulates real-world cyber attacks to exploit vulnerabilities identified during the vulnerability assessment. Penetration testing helps to understand the impact of exploiting these vulnerabilities and assesses the overall security posture of the organization.
Why is VAPT Important?
Stay Ahead of Threats: VAPT keeps organizations updated on emerging threats and vulnerabilities, enabling proactive measures to defend against new attack vectors.
Identify Security Weaknesses: VAPT helps in identifying and cataloging vulnerabilities in an organization’s IT environment, allowing for timely remediation before they can be exploited by attackers.
Protect Sensitive Data: By uncovering and addressing security flaws, VAPT helps protect sensitive data such as personal information, financial records, and intellectual property.
Meet Compliance Requirements: Many regulatory frameworks and standards, such as GDPR, HIPAA, PCI DSS, and ISO 27001, require regular VAPT to ensure compliance with security requirements.
Improve Security Posture: VAPT provides insights into the effectiveness of existing security controls and highlights areas for improvement, thereby enhancing the overall security posture.
Prevent Financial Loss: By mitigating vulnerabilities, organizations can prevent data breaches and cyber-attacks, which can result in significant financial losses due to downtime, legal penalties, and damage to reputation.
Maintain Customer Trust: Regular VAPT demonstrates a commitment to security, helping to maintain customer trust and confidence in the organization’s ability to protect their data.
How Regularly Should VAPT be Conducted?
As a best practice standard, the frequency of VAPT should be based on several factors, including the organization’s size, industry, regulatory requirements, and risk tolerance. Here are some general guidelines:
Compliance Requirements: Follow industry-specific regulations and compliance requirements, which may mandate more frequent testing (e.g., quarterly for PCI DSS).
Regular Intervals: Conduct VAPT at least once or twice a year as a standard practice.
After Major Changes: Perform VAPT after significant changes to the IT infrastructure, such as deploying new applications, systems, or major updates.
Post-Incident: Conduct VAPT following any security incident or data breach to identify the root cause and prevent future occurrences.
What domains should be covered for Vulnerability Assessment (VA) and Penetration Testing (PT)?
Vulnerability Assessment and Penetration Testing (VAPT) should be performed across various domains to ensure comprehensive security coverage. Here are key domains where VAPT should be conducted:
- Web Applications:
- VA: Identify and catalog security weaknesses such as outdated libraries, insecure configurations, and known vulnerabilities.
- PT: Conduct simulated attacks to exploit vulnerabilities like SQL injection, XSS, and authentication bypasses.
- Network Infrastructure:
- VA: Scan network devices like routers, switches, and firewalls for known vulnerabilities and misconfigurations.
- PT: Perform penetration tests on network devices to exploit vulnerabilities and identify potential entry points.
- Mobile Applications:
- VA: Analyze mobile apps for security flaws such as insecure data storage, improper session handling, and known vulnerabilities.
- PT: Conduct manual testing to exploit vulnerabilities in mobile apps, such as insecure data transmission and weak authentication.
- Cloud Environments:
- VA: Assess cloud services and infrastructure for configuration issues, policy violations, and known vulnerabilities.
- PT: Simulate attacks on cloud infrastructure to exploit misconfigurations, insecure APIs, and weak access controls.
- Databases:
- VA: Check databases for vulnerabilities like unpatched systems, misconfigurations, and weak access controls.
- PT: Perform penetration tests on databases to exploit vulnerabilities such as SQL injection and privilege escalation.
- APIs:
- VA: Assess APIs for issues like improper authentication, rate limiting, and known security flaws.
- PT: Conduct penetration tests to exploit vulnerabilities in APIs, such as unauthorized access and injection flaws.
- IoT Devices:
- VA: Scan IoT devices for known vulnerabilities, firmware issues, and insecure configurations.
- PT: Perform attacks on IoT devices to exploit firmware vulnerabilities, insecure communication, and weak authentication.
- Wireless Networks:
- VA: Analyze wireless network configurations and encryption protocols for weaknesses.
- PT: Conduct penetration tests on wireless networks to exploit vulnerabilities such as WPA cracking and rogue access points.
- Endpoints:
- VA: Identify vulnerabilities in workstations, laptops, and other endpoints such as missing patches and insecure settings.
- PT: Simulate attacks on endpoints to exploit vulnerabilities like malware infections, privilege escalation, and lateral movement.
- Industrial Control Systems (ICS):
- VA: Assess ICS/SCADA systems for known vulnerabilities and misconfigurations.
- PT: Perform penetration tests on ICS/SCADA systems to identify and exploit vulnerabilities that could impact critical infrastructure.
Access0day’s Assessment Approach
| Sl No. | Category | Objectives | OWASP Top 10 | CWE |
| 1 | Information Gathering | Conduct Search Engine Discovery Reconnaissance for Information Leakage | A1 | CWE-200 |
| 2 | Information Gathering | Conduct Search Engine Discovery Reconnaissance for Information Leakage | A1 | CWE-200 |
| 3 | Information Gathering | Conduct Search Engine Discovery Reconnaissance for Information Leakage | A5 | CWE-200 |
| 4 | Information Gathering | Conduct Search Engine Discovery Reconnaissance for Information Leakage | A1 | CWE-200 |
| 5 | Information Gathering | Conduct Search Engine Discovery Reconnaissance for Information Leakage | A1 | CWE-200 |
| 6 | Information Gathering | Fingerprint Web Server | A5 A6 | CWE-756 CWE-1352 |
| 7 | Information Gathering | Review Webserver Metafiles for Information Leakage | A1 | CWE-200 |
| 8 | Information Gathering | Enumerate Applications on Webserver | A5 | CWE-200 |
| 9 | Information Gathering | Review Webpage Content for Information Leakage | A1 | CWE-200 CWE-540 |
| 10 | Information Gathering | Review Webpage Content for Information Leakage | A1 | CWE-200 CWE-540 |
| 11 | Information Gathering | Review Webpage Content for Information Leakage | A1 | CWE-200 CWE-540 |
| 12 | Information Gathering | Identify Application Entry Points | A7 | CWE-693 |
| 13 | Information Gathering | Map Execution Paths Through Application | A4 | CWE-200 |
| 14 | Information Gathering | Fingerprint Web Application Framework | A5 A6 | CWE-756 CWE-1104 |
| 15 | Information Gathering | Fingerprint Web Application Framework | A5 A6 | CWE-756 CWE-1104 |
| 16 | Configuration and Deploy Management Testing | Test Network Infrastructure Configuration | A1 A5 A6 | CWE-284 CWE-1349 CWE-1352 |
| 17 | Configuration and Deploy Management Testing | Test Network Infrastructure Configuration | A1 A5 A6 | CWE-284 CWE-1349 CWE-1352 |
| 18 | Configuration and Deploy Management Testing | Test Network Infrastructure Configuration | A1 A5 A6 | CWE-284 CWE-1349 CWE-1352 |
| 19 | Configuration and Deploy Management Testing | Test Network Infrastructure Configuration | A1 A5 A6 | CWE-284 CWE-1349 CWE-1352 |
| 20 | Configuration and Deploy Management Testing | Test Network Infrastructure Configuration | A1 A5 A6 | CWE-284 CWE-1349 CWE-1352 |
| 21 | Configuration and Deploy Management Testing | Test Network Infrastructure Configuration | A1 A5 A6 | CWE-284 CWE-1349 CWE-1352 |
| 22 | Configuration and Deploy Management Testing | Test Application Platform Configuration | A1 A5 A9 | CWE-13 CWE-117 CWE-223 CWE-200 CWE-201 CWE-489 CWE-532 CWE-548 CWE-651 CWE-778 |
| 23 | Configuration and Deploy Management Testing | Test Application Platform Configuration | A1 A5 A9 | CWE-13 CWE-117 CWE-223 CWE-200 CWE-201 CWE-489 CWE-532 CWE-548 CWE-651 CWE-778 |
| 24 | Configuration and Deploy Management Testing | Test Application Platform Configuration | A1 A5 A9 | CWE-13 CWE-117 CWE-223 CWE-200 CWE-201 CWE-489 CWE-532 CWE-548 CWE-651 CWE-778 |
| 25 | Configuration and Deploy Management Testing | Test Application Platform Configuration | A1 A5 A9 | CWE-13 CWE-117 CWE-223 CWE-200 CWE-201 CWE-489 CWE-532 CWE-548 CWE-651 CWE-778 |
| 26 | Configuration and Deploy Management Testing | Test Application Platform Configuration | A1 A5 A9 | CWE-13 CWE-117 CWE-223 CWE-200 CWE-201 CWE-489 CWE-532 CWE-548 CWE-651 CWE-778 |
| 27 | Configuration and Deploy Management Testing | Test Application Platform Configuration | A1 A5 A9 | CWE-13 CWE-117 CWE-223 CWE-200 CWE-201 CWE-489 CWE-532 CWE-548 CWE-651 CWE-778 |
| 28 | Configuration and Deploy Management Testing | Test File Extensions Handling for Sensitive Information | A1 | CWE-200 CWE-425 CWE-552 |
| 29 | Configuration and Deploy Management Testing | Test File Extensions Handling for Sensitive Information | A1 | CWE-200 CWE-425 CWE-552 |
| 30 | Configuration and Deploy Management Testing | Review Old Backup and Unreferenced Files for Sensitive Information | A1 | CWE-200 CWE-531 CWE-538 |
| 31 | Configuration and Deploy Management Testing | Enumerate Infrastructure and Application Admin Interfaces | A1 A4 | CWE-284 CWE-419 |
| 32 | Configuration and Deploy Management Testing | Test HTTP Methods | A5 | CWE-650 CWE-749 |
| 33 | Configuration and Deploy Management Testing | Test HTTP Methods | A5 | CWE-650 CWE-749 |
| 34 | Configuration and Deploy Management Testing | Test HTTP Methods | A5 | CWE-650 CWE-749 |
| 35 | Configuration and Deploy Management Testing | Test HTTP Strict Transport Security | A5 | CWE-523 |
| 36 | Configuration and Deploy Management Testing | Test RIA Cross Domain Policy | A5 | CWE-942 |
| 37 | Configuration and Deploy Management Testing | Test File Permission | A1 A5 | CWE-552 CWE-732 |
| 38 | Configuration and Deploy Management Testing | Test Cloud Storage | A1 | CWE-264 |
| 39 | Configuration and Deploy Management Testing | Testing for Content Security Policy | A5 | CWE-1021 |
| 40 | Configuration and Deploy Management Testing | Fuzzing | A1 A4 | CWE-200 CWE-419 |
| 41 | Configuration and Deploy Management Testing | Fuzzing | A1 A4 | CWE-200 CWE-419 |
| 42 | Configuration and Deploy Management Testing | Security Best Practices | A2 A4 A5 | CWE-532 CWE-312 CWE-313 |
| 43 | Configuration and Deploy Management Testing | Security Best Practices | A2 A4 A5 | CWE-312 CWE-313 CWE-523 |
| 44 | Configuration and Deploy Management Testing | Security Best Practices | A2 A4 A5 | CWE-313 CWE-315 |
| 45 | Configuration and Deploy Management Testing | Security Best Practices | A2 A4 A5 | CWE-315 |
| 46 | Configuration and Deploy Management Testing | Security Best Practices | A2 A4 A5 | CWE-348 |
| 47 | Configuration and Deploy Management Testing | Security Best Practices | A2 A4 A5 | CWE-307 |
| 48 | Configuration and Deploy Management Testing | Security Best Practices | A2 A4 A5 | CWE-400 CWE-770 |
| 49 | Configuration and Deploy Management Testing | Security Best Practices | A2 A4 A5 | CWE-326 |
| 50 | Configuration and Deploy Management Testing | Security Best Practices | A2 A4 A5 | CWE-326 |
| 51 | Configuration and Deploy Management Testing | Security Best Practices | A2 A4 A5 | CWE-358 CWE-531 |
| 52 | Configuration and Deploy Management Testing | Open Redirection | A2 A4 A5 | CWE-601 |
| 53 | Configuration and Deploy Management Testing | Open Redirection | A2 A4 A5 | CWE-601 |
| 54 | Configuration and Deploy Management Testing | Missing Security Headers | A5 | CWE-693 |
| 55 | Configuration and Deploy Management Testing | Information Disclosure in Headers | A5 | CWE-200 CWE-798 CWE-521 CWE-522 CWE-538 CWE-311 |
| 56 | Configuration and Deploy Management Testing | Information Disclosure in Headers | A5 | CWE-200 |
| 57 | Configuration and Deploy Management Testing | Rate Limit Scenarios | A5 | CWE-770 |
| 58 | Configuration and Deploy Management Testing | Rate Limit Scenarios | A5 | CWE-770 CWE-770 |
| 59 | Configuration and Deploy Management Testing | Security Misconfigurations | A5 | CWE-451 |
| 60 | Configuration and Deploy Management Testing | Security Misconfigurations | A5 | CWE-829 |
| 61 | Configuration and Deploy Management Testing | Security Misconfigurations | A5 | CWE-59 |
| 62 | Configuration and Deploy Management Testing | Security Misconfigurations | A5 | CWE-306 |
| 63 | Configuration and Deploy Management Testing | Security Misconfigurations | A5 | CWE-942 |
| 64 | Configuration and Deploy Management Testing | Security Misconfigurations | A5 | CWE-942 |
| 65 | Identity Management Testing | Test Role Definitions | A4 | CWE-266 CWE-269 |
| 66 | Identity Management Testing | Test Role Definitions | A4 | CWE-266 CWE-269 |
| 67 | Identity Management Testing | Test Role Definitions | A4 | CWE-266 CWE-269 |
| 68 | Identity Management Testing | Test Role Definitions | A4 | CWE-266 CWE-269 |
| 69 | Identity Management Testing | Test Role Definitions | A4 | CWE-266 CWE-269 |
| 70 | Identity Management Testing | Test Role Definitions | A4 | CWE-266 CWE-269 |
| 71 | Identity Management Testing | Test User Registration Process | A4 | CWE-266 CWE-269 |
| 72 | Identity Management Testing | Test User Registration Process | A4 | CWE-419 |
| 73 | Identity Management Testing | Test User Registration Process | A4 | CWE-419 |
| 74 | Identity Management Testing | Test User Registration Process | A4 | CWE-419 |
| 75 | Identity Management Testing | Test User Registration Process | A4 | CWE-419 |
| 76 | Identity Management Testing | Test User Registration Process | A4 | CWE-419 |
| 77 | Identity Management Testing | Test User Registration Process | A4 | CWE-419 |
| 78 | Identity Management Testing | Test User Registration Process | A4 | CWE-419 |
| 79 | Identity Management Testing | Test User Registration Process | A4 | CWE-419 |
| 80 | Identity Management Testing | Test User Registration Process | A4 | CWE-419 |
| 81 | Identity Management Testing | Test User Registration Process | A4 | CWE-419 |
| 82 | Identity Management Testing | Test User Registration Process | A4 | CWE-419 |
| 83 | Identity Management Testing | Testing for Account Enumeration and Guessable User Account | A7 | CWE-204 |
| 84 | Identity Management Testing | Testing for Account Enumeration and Guessable User Account | A7 | CWE-204 |
| 85 | Authentication Testing | Testing for Default Credentials | A7 | CWE-1392 |
| 86 | Authentication Testing | Testing for Weak Lock Out Mechanism | A7 | CWE-307 |
| 87 | Authentication Testing | Testing for Weak Lock Out Mechanism | A7 | CWE-307 |
| 88 | Authentication Testing | Testing for Bypassing Authentication Schema | A1 A7 | CWE-287 CWE-288 CWE-290 CWE-294 CWE-302 CWE-304 CWE-306 CWE-425 CWE-804 |
| 89 | Authentication Testing | Testing for Bypassing Authentication Schema | A1 A7 | CWE-287 CWE-288 CWE-290 CWE-294 CWE-302 CWE-304 CWE-306 CWE-425 CWE-804 |
| 90 | Authentication Testing | Testing for Bypassing Authentication Schema | A1 A7 | CWE-287 CWE-288 CWE-290 CWE-294 CWE-302 CWE-304 CWE-306 CWE-425 CWE-804 |
| 91 | Authentication Testing | Testing for Bypassing Authentication Schema | A1 A7 | CWE-287 CWE-288 CWE-290 CWE-294 CWE-302 CWE-304 CWE-306 CWE-425 CWE-804 |
| 92 | Authentication Testing | Testing for Bypassing Authentication Schema | A1 A7 | CWE-287 CWE-288 CWE-290 CWE-294 CWE-302 CWE-304 CWE-306 CWE-425 CWE-804 |
| 93 | Authentication Testing | Testing for Vulnerable Remember Password | A4 A5 | CWE-315 CWE-522 CWE-524 |
| 94 | Authentication Testing | Testing for Vulnerable Remember Password | A4 A5 | CWE-315 CWE-522 CWE-524 |
| 95 | Authentication Testing | Testing for Browser Cache Weaknesses | A4 | CWE-525 |
| 96 | Authentication Testing | Testing for Weak Password Policy | A7 | CWE-521 CWE-1391 |
| 97 | Authentication Testing | Testing for Weak Password Policy | A7 | CWE-521 CWE-1391 |
| 98 | Authentication Testing | Testing for Weak Password Policy | A7 | CWE-521 CWE-1391 |
| 99 | Authentication Testing | Testing for Weak Password Policy | A7 | CWE-521 CWE-1391 |
| 100 | Authentication Testing | Testing for Weak Security Question Answer | A7 | CWE-640 |
| 101 | Authentication Testing | Testing for Weak Security Question Answer | A7 | CWE-640 |
| 102 | Authentication Testing | Testing for Weak Security Question Answer | A7 | CWE-640 |
| 103 | Authentication Testing | Testing for Weak Password Change or Reset Functionalities | A7 | CWE-620 CWE-640 |
| 104 | Authentication Testing | Testing for Weak Password Change or Reset Functionalities | A7 | CWE-620 CWE-640 |
| 105 | Authentication Testing | Testing for Weak Password Change or Reset Functionalities | A7 | CWE-620 CWE-640 |
| 106 | Authentication Testing | Testing for Weak Password Change or Reset Functionalities | A7 | CWE-620 CWE-640 |
| 107 | Authentication Testing | Testing for Weak Password Change or Reset Functionalities | A7 | CWE-620 CWE-640 |
| 108 | Authentication Testing | Testing for Weak Password Change or Reset Functionalities | A7 | CWE-620 CWE-640 |
| 109 | Authentication Testing | Testing for Weak Password Change or Reset Functionalities | A7 | CWE-620 CWE-640 |
| 110 | Authentication Testing | Testing for Weak Password Change or Reset Functionalities | A7 | CWE-620 CWE-640 |
| 111 | Authentication Testing | Testing for Weak Password Change or Reset Functionalities | A7 | CWE-620 CWE-640 |
| 112 | Authentication Testing | Testing for Weak Password Change or Reset Functionalities | A7 | CWE-620 CWE-640 |
| 113 | Authentication Testing | Testing for Weak Password Change or Reset Functionalities | A7 | CWE-620 CWE-640 |
| 114 | Authentication Testing | Testing for Weak Password Change or Reset Functionalities | A7 | CWE-620 CWE-640 |
| 115 | Authentication Testing | Testing for Weak Password Change or Reset Functionalities | A7 | CWE-620 CWE-640 |
| 116 | Authentication Testing | Testing for Weak Password Change or Reset Functionalities | A7 | CWE-620 CWE-640 |
| 117 | Authentication Testing | Testing for Weak Password Change or Reset Functionalities | A7 | CWE-620 CWE-640 |
| 118 | Authentication Testing | Testing for Weak Password Change or Reset Functionalities | A7 | CWE-620 CWE-640 |
| 119 | Authentication Testing | Testing for Weak Password Change or Reset Functionalities | A7 | CWE-620 CWE-640 |
| 120 | Authentication Testing | Testing for Weak Password Change or Reset Functionalities | A7 | CWE-620 CWE-640 |
| 121 | Authentication Testing | Testing for Weaker Authentication in Alternative Channel | A7 | CWE-288 |
| 122 | Authentication Testing | Testing for Weaker Authentication in Alternative Channel | A7 | CWE-288 |
| 123 | Authentication Testing | Testing Multi-Factor Authentication (MFA) | A7 | CWE-288 CWE-304 CWE-308 |
| 124 | Authentication Testing | Testing Multi-Factor Authentication (MFA) | A7 | CWE-288 CWE-304 CWE-308 |
| 125 | Authentication Testing | Testing Multi-Factor Authentication (MFA) | A7 | CWE-288 CWE-304 CWE-308 |
| 126 | Authentication Testing | Testing Multi-Factor Authentication (MFA) | A7 | CWE-288 CWE-304 CWE-308 |
| 127 | Authentication Testing | Testing Multi-Factor Authentication (MFA) | A7 | CWE-288 CWE-304 CWE-308 |
| 128 | Authentication Testing | Testing Multi-Factor Authentication (MFA) | A7 | CWE-288 CWE-304 CWE-308 |
| 129 | Authentication Testing | Testing Multi-Factor Authentication (MFA) | A7 | CWE-288 CWE-304 CWE-308 |
| 130 | Authentication Testing | Testing Multi-Factor Authentication (MFA) | A7 | CWE-288 CWE-304 CWE-308 |
| 131 | Authentication Testing | Testing Multi-Factor Authentication (MFA) | A7 | CWE-288 CWE-304 CWE-308 |
| 132 | Authentication Testing | Testing Multi-Factor Authentication (MFA) | A7 | CWE-288 CWE-304 CWE-308 |
| 133 | Authentication Testing | Testing Multi-Factor Authentication (MFA) | A7 | CWE-288 CWE-304 CWE-308 |
| 134 | Authentication Testing | Testing Multi-Factor Authentication (MFA) | A7 | CWE-288 CWE-304 CWE-308 |
| 135 | Authentication Testing | Testing Multi-Factor Authentication (MFA) | A7 | CWE-288 CWE-304 CWE-308 |
| 136 | Authorization Testing | Testing Directory Traversal File Include | A1 | CWE-22 CWE-23 CWE-35 CWE-829 |
| 137 | Authorization Testing | Testing Directory Traversal File Include | A1 | CWE-22 CWE-23 CWE-35 CWE-829 |
| 138 | Authorization Testing | Testing for Bypassing Authorization Schema | A1 | CWE-285 CWE-732 CWE-862 CWE-863 |
| 139 | Authorization Testing | Testing for Bypassing Authorization Schema | A1 | CWE-285 CWE-732 CWE-862 CWE-863 |
| 140 | Authorization Testing | Testing for Privilege Escalation | A1 | CWE-269 CWE-639 |
| 141 | Authorization Testing | Testing for Privilege Escalation | A1 | CWE-269 CWE-639 |
| 142 | Authorization Testing | Testing for Privilege Escalation | A1 | CWE-269 CWE-639 |
| 143 | Authorization Testing | Testing for Insecure Direct Object References | A1 | CWE-639 |
| 144 | Authorization Testing | Testing for Insecure Direct Object References | A1 | CWE-639 |
| 145 | Authorization Testing | Testing for Insecure Direct Object References | A1 | CWE-639 |
| 146 | Authorization Testing | Testing for Insecure Direct Object References | A1 | CWE-639 |
| 147 | Authorization Testing | Testing for Insecure Direct Object References | A1 | CWE-639 |
| 148 | Authorization Testing | Testing for Insecure Direct Object References | A1 | CWE-639 |
| 149 | Authorization Testing | Testing for Insecure Direct Object References | A1 | CWE-639 |
| 150 | Authorization Testing | Testing for Insecure Direct Object References | A1 | CWE-639 |
| 151 | Authorization Testing | Testing for OAuth Weaknesses | A1 | CWE-290 CWE-345 CWE-798 |
| 152 | Authorization Testing | Testing for OAuth Weaknesses | A1 | CWE-290 CWE-345 CWE-798 |
| 153 | Authorization Testing | Testing for OAuth Weaknesses | A1 | CWE-290 CWE-345 CWE-798 |
| 154 | Session Management Testing | Testing for Session Management Schema | A2 A4 | CWE-315 CWE-330 CWE-539 CWE-694 |
| 155 | Session Management Testing | Testing for Session Management Schema | A2 A4 | CWE-315 CWE-330 CWE-539 CWE-694 |
| 156 | Session Management Testing | Testing for Session Management Schema | A2 A4 | CWE-315 CWE-330 CWE-539 CWE-694 |
| 157 | Session Management Testing | Testing for Session Management Schema | A2 A4 | CWE-315 CWE-330 CWE-539 CWE-694 |
| 158 | Session Management Testing | Testing for Session Management Schema | A2 A4 | CWE-315 CWE-330 CWE-539 CWE-694 |
| 159 | Session Management Testing | Testing for Session Management Schema | A2 A4 | CWE-315 CWE-330 CWE-539 CWE-694 |
| 160 | Session Management Testing | Testing for Cookies Attributes | A5 | CWE-16 CWE-614 CWE-1004 CWE-1275 |
| 161 | Session Management Testing | Testing for Session Fixation | A7 | CWE-384 |
| 162 | Session Management Testing | Testing for Session Fixation | A7 | CWE-384 |
| 163 | Session Management Testing | Testing for Session Fixation | A7 | CWE-384 |
| 164 | Session Management Testing | Testing for Exposed Session Variables | A7 | CWE-598 |
| 165 | Session Management Testing | Testing for Exposed Session Variables | A7 | CWE-598 |
| 166 | Session Management Testing | Testing for Exposed Session Variables | A7 | CWE-598 |
| 167 | Session Management Testing | Testing for Exposed Session Variables | A7 | CWE-598 |
| 168 | Session Management Testing | Testing for Cross Site Request Forgery | A1 | CWE-352 |
| 169 | Session Management Testing | Testing for Cross Site Request Forgery | A1 | CWE-352 |
| 170 | Session Management Testing | Testing for Cross Site Request Forgery | A1 | CWE-352 |
| 171 | Session Management Testing | Testing for Cross Site Request Forgery | A1 | CWE-352 |
| 172 | Session Management Testing | Testing for Cross Site Request Forgery | A1 | CWE-352 |
| 173 | Session Management Testing | Testing for Logout Functionality | A7 | CWE-613 |
| 174 | Session Management Testing | Testing for Logout Functionality | A7 | CWE-613 |
| 175 | Session Management Testing | Testing for Logout Functionality | A7 | CWE-613 |
| 176 | Session Management Testing | Testing for Logout Functionality | A7 | CWE-613 |
| 177 | Session Management Testing | Testing Session Timeout | A7 | CWE-613 |
| 178 | Session Management Testing | Testing for Session Puzzling | A7 | CWE-841 |
| 179 | Session Management Testing | Testing for Session Hijacking | A2 | CWE-523 |
| 180 | Session Management Testing | Testing JSON Web Tokens | A7 | CWE-345 CWE-757 CWE-798 |
| 181 | Session Management Testing | Testing JSON Web Tokens | A7 | CWE-345 CWE-757 CWE-798 |
| 182 | Session Management Testing | Testing JSON Web Tokens | A7 | CWE-345 CWE-757 CWE-798 |
| 183 | Session Management Testing | Testing JSON Web Tokens | A7 | CWE-345 CWE-757 CWE-798 |
| 184 | Session Management Testing | Testing JSON Web Tokens | A7 | CWE-345 CWE-757 CWE-798 |
| 185 | Session Management Testing | Testing JSON Web Tokens | A7 | CWE-345 CWE-757 CWE-798 |
| 186 | Data Validation Testing | Testing for Reflected Cross Site Scripting | A3 | CWE-79 |
| 187 | Data Validation Testing | Testing for Reflected Cross Site Scripting | A3 | CWE-79 |
| 188 | Data Validation Testing | Testing for Reflected Cross Site Scripting | A3 | CWE-79 |
| 189 | Data Validation Testing | Testing for Reflected Cross Site Scripting | A3 | CWE-79 |
| 190 | Data Validation Testing | Testing for Stored Cross Site Scripting | A3 | CWE-79 |
| 191 | Data Validation Testing | Testing for Stored Cross Site Scripting | A3 | CWE-79 |
| 192 | Data Validation Testing | Testing for Stored Cross Site Scripting | A3 | CWE-79 |
| 193 | Data Validation Testing | Testing for HTTP Parameter Pollution | A3 | CWE-235 |
| 194 | Data Validation Testing | Testing for HTTP Parameter Pollution | A3 | CWE-235 |
| 195 | Data Validation Testing | Testing for SQL Injection | A3 | CWE-89 |
| 196 | Data Validation Testing | Testing for SQL Injection | A3 | CWE-89 |
| 197 | Data Validation Testing | Testing for SQL Injection | A3 | CWE-89 |
| 198 | Data Validation Testing | Testing for SQL Injection | A3 | CWE-89 |
| 199 | Data Validation Testing | Testing for LDAP Injection | A3 | CWE-90 |
| 200 | Data Validation Testing | Testing for XML Injection | A5 | CWE-91 CWE-611 CWE-652 |
| 201 | Data Validation Testing | Testing for XML Injection | A5 | CWE-91 CWE-611 CWE-652 |
| 202 | Data Validation Testing | Testing for SSI Injection | A3 | CWE-97 |
| 203 | Data Validation Testing | Testing for XPath Injection | A3 | CWE-91 CWE-643 |
| 204 | Data Validation Testing | Testing for IMAP SMTP Injection | A3 | CWE-147 |
| 205 | Data Validation Testing | Testing for Code Injection | A3 | CWE-22 CWE-94 CWE-95 CWE-98 CWE-829 |
| 206 | Data Validation Testing | Testing for Code Injection | A3 | CWE-22 CWE-94 CWE-95 CWE-98 CWE-829 |
| 207 | Data Validation Testing | Testing for Code Injection | A3 | CWE-22 CWE-94 CWE-95 CWE-98 CWE-829 |
| 208 | Data Validation Testing | Testing for Code Injection | A3 | CWE-22 CWE-94 CWE-95 CWE-98 CWE-829 |
| 209 | Data Validation Testing | Testing for Command Injection | A3 | CWE-77 CWE-78 |
| 210 | Data Validation Testing | Testing for HTTP Splitting Smuggling | A3 A4 | CWE-93 CWE-113 CWE-444 |
| 211 | Data Validation Testing | Testing for HTTP Splitting Smuggling | A3 A4 | CWE-93 CWE-113 CWE-444 |
| 212 | Data Validation Testing | Testing for Host Header Injection | A4 | CWE-74 CWE-116 |
| 213 | Data Validation Testing | Testing for Host Header Injection | A4 | CWE-74 CWE-116 |
| 214 | Data Validation Testing | Testing for Host Header Injection | A4 | CWE-74 CWE-116 |
| 215 | Data Validation Testing | Testing for Host Header Injection | A4 | CWE-74 CWE-116 |
| 216 | Data Validation Testing | Testing for Host Header Injection | A4 | CWE-74 CWE-116 |
| 217 | Data Validation Testing | Testing for Host Header Injection | A4 | CWE-74 CWE-116 |
| 218 | Data Validation Testing | Testing for Server-side Template Injection | A4 | CWE-1336 |
| 219 | Data Validation Testing | Testing for Server-side Template Injection | A4 | CWE-1336 |
| 220 | Data Validation Testing | Testing for Server-Side Request Forgery | A10 | CWE-918 |
| 221 | Data Validation Testing | Testing for Server-Side Request Forgery | A10 | CWE-918 |
| 222 | Data Validation Testing | Testing for Mass Assignment | A4 | CWE-915 |
| 223 | Data Validation Testing | Testing for Mass Assignment | A4 | CWE-915 |
| 224 | Error Handling | Testing for Improper Error Handling | A5 | CWE-209 CWE-210 CWE-431 CWE-497 CWE-544 CWE-550 CWE-728 |
| 225 | Cryptography | Testing for Weak Transport Layer Security | A2 A7 | CWE-295 CWE-296 CWE-297 CWE-298 CWE-319 CWE-326 CWE-327 CWE-310 CWE-757 |
| 226 | Cryptography | Testing for Padding Oracle | A2 | CWE-326 CWE-649 |
| 227 | Cryptography | Testing for Padding Oracle | A2 | CWE-326 CWE-649 |
| 228 | Cryptography | Testing for Sensitive Information Sent via Unencrypted Channels | A2 | CWE-311 CWE-319 CWE-523 |
| 229 | Cryptography | Testing for Sensitive Information Sent via Unencrypted Channels | A2 | CWE-311 CWE-319 CWE-523 |
| 230 | Cryptography | Testing for Sensitive Information Sent via Unencrypted Channels | A2 | CWE-311 CWE-319 CWE-523 |
| 231 | Cryptography | Testing for Weak Encryption | A2 | CWE-261 CWE-320 CWE-321 CWE-322 CWE-323 CWE-324 CWE-325 CWE-326 CWE-327 CWE-328 CWE-329 CWE-330 CWE-331 CWE-335 CWE-336 CWE-337 CWE-338 CWE-340 CWE-347 CWE-354 CWE-759 CWE-760 CWE-780 CWE-798 CWE-916 |
| 232 | Business logic Testing | Test Business Logic Data Validation | A4 | CWE-840 |
| 233 | Business logic Testing | Test Business Logic Data Validation | A4 | CWE-840 |
| 234 | Business logic Testing | Test Business Logic Data Validation | A4 | CWE-840 |
| 235 | Business logic Testing | Test Ability to Forge Requests | A4 | CWE-840 |
| 236 | Business logic Testing | Test Ability to Forge Requests | A4 | CWE-840 |
| 237 | Business logic Testing | Test Ability to Forge Requests | A4 | CWE-840 |
| 238 | Business logic Testing | Test Ability to Forge Requests | A4 | CWE-840 |
| 239 | Business logic Testing | Source Code Analysis | A1 A4 | CWE-200 TBU |
| 240 | Business logic Testing | Source Code Analysis | A1 A4 | CWE-200 TBU |
| 241 | Business logic Testing | Source Code Analysis | A1 A4 | CWE-200 TBU |
| 242 | Business logic Testing | Cloud Related Vulnerabilities | A1 A4 | CWE-200 CWE-204 |
| 243 | Business logic Testing | Cloud Related Vulnerabilities | A1 A4 | CWE-862 |
| 244 | Business logic Testing | Cloud Related Vulnerabilities | A1 A4 | CWE-200 CWE-798 CWE-312 |
| 245 | Business logic Testing | Cloud Related Vulnerabilities | A1 A4 | CWE-918 CWE-829 |
| 246 | Business logic Testing | Cloud Related Vulnerabilities | A1 A4 | CWE-538 |
| 247 | Business logic Testing | Cloud Related Vulnerabilities | A1 A4 | CWE-287 |
| 248 | Business logic Testing | Cloud Related Vulnerabilities | A1 A4 | CWE-284 CWE-358 |
| 249 | Business logic Testing | Cloud Related Vulnerabilities | A1 A4 | CWE-613 |
| 250 | Business logic Testing | Test Integrity Checks | A4 | CWE-840 CWE-472 |
| 251 | Business logic Testing | Test Integrity Checks | A4 | CWE-840 CWE-472 |
| 252 | Business logic Testing | Test Integrity Checks | A4 | CWE-840 CWE-472 |
| 253 | Business logic Testing | Test Integrity Checks | A4 | CWE-840 CWE-472 |
| 254 | Business logic Testing | Test for Process Timing | A4 | CWE-840 CWE-362 |
| 255 | Business logic Testing | Test for Process Timing | A4 | CWE-840 CWE-362 |
| 256 | Business logic Testing | Test Number of Times a Function Can Be Used Limits | A4 A7 | CWE-799 |
| 257 | Business logic Testing | Test Number of Times a Function Can Be Used Limits | A4 A7 | CWE-799 |
| 258 | Business logic Testing | Test Number of Times a Function Can Be Used Limits | A4 A7 | CWE-799 |
| 259 | Business logic Testing | Test Number of Times a Function Can Be Used Limits | A4 A7 | CWE-799 |
| 260 | Business logic Testing | Testing for the Circumvention of Work Flows | A4 | CWE-841 |
| 261 | Business logic Testing | Testing for the Circumvention of Work Flows | A4 | CWE-841 |
| 262 | Business logic Testing | Test Defenses Against Application Misuse | A4 | CWE-693 |
| 263 | Business logic Testing | Test Defenses Against Application Misuse | A4 | CWE-693 |
| 264 | Business logic Testing | Test Upload of Unexpected File Types | A4 | CWE-434 CWE-602 |
| 265 | Business logic Testing | Test Upload of Unexpected File Types | A4 | CWE-434 CWE-602 |
| 266 | Business logic Testing | Test Upload of Unexpected File Types | A4 | CWE-434 CWE-602 |
| 267 | Business logic Testing | Test Upload of Unexpected File Types | A4 | CWE-434 CWE-602 |
| 268 | Business logic Testing | Test Upload of Unexpected File Types | A4 | CWE-434 CWE-602 |
| 269 | Business logic Testing | Test Upload of Unexpected File Types | A4 | CWE-434 CWE-602 |
| 270 | Business logic Testing | Test Upload of Unexpected File Types | A4 | CWE-434 CWE-602 |
| 271 | Business logic Testing | Test Upload of Unexpected File Types | A4 | CWE-434 CWE-602 |
| 272 | Business logic Testing | Test Upload of Unexpected File Types | A4 | CWE-434 CWE-602 |
| 273 | Business logic Testing | Test Upload of Unexpected File Types | A4 | CWE-434 CWE-602 |
| 274 | Business logic Testing | Test Upload of Malicious Files | A4 | CWE-434 |
| 275 | Business logic Testing | Test Upload of Malicious Files | A4 | CWE-434 |
| 276 | Business logic Testing | Test Upload of Malicious Files | A4 | CWE-434 |
| 277 | Business logic Testing | Test Upload of Malicious Files | A4 | CWE-434 |
| 278 | Business logic Testing | Test Upload of Malicious Files | A4 | CWE-434 |
| 279 | Business logic Testing | Test Upload of Malicious Files | A4 | CWE-434 |
| 280 | Business logic Testing | Test Payment Functionality | A4 | CWE-472 CWE-602 CWE-807 |
| 281 | Business logic Testing | Test Payment Functionality | A4 | CWE-472 CWE-602 CWE-807 |
| 282 | Business logic Testing | Test Payment Functionality | A4 | CWE-472 CWE-602 CWE-807 |
| 283 | Client Side Testing | Testing for DOM-Based Cross Site Scripting | A3 | CWE-79 |
| 284 | Client Side Testing | Testing for DOM-Based Cross Site Scripting | A3 | CWE-79 |
| 285 | Client Side Testing | Testing for JavaScript Execution | A3 | CWE-79 |
| 286 | Client Side Testing | Testing for HTML Injection | A3 | CWE-80 |
| 287 | Client Side Testing | Testing for Client-side URL Redirect | A4 | CWE-601 |
| 288 | Client Side Testing | Testing for Client-side URL Redirect | A4 | CWE-601 |
| 289 | Client Side Testing | Testing for CSS Injection | A3 | CWE-20 |
| 290 | Client Side Testing | Testing for CSS Injection | A3 | CWE-20 |
| 291 | Client Side Testing | Testing for Client-side Resource Manipulation | A3 | CWE-20 |
| 292 | Client Side Testing | Testing for Client-side Resource Manipulation | A3 | CWE-20 |
| 293 | Client Side Testing | Testing Cross Origin Resource Sharing | A5 | CWE-942 |
| 294 | Client Side Testing | Testing Cross Origin Resource Sharing | A5 | CWE-942 |
| 295 | Client Side Testing | Testing Cross Origin Resource Sharing | A5 | CWE-942 |
| 296 | Client Side Testing | Testing Cross Origin Resource Sharing | A5 | CWE-942 |
| 297 | Client Side Testing | Testing Cross Origin Resource Sharing | A5 | CWE-942 |
| 298 | Client Side Testing | Testing Cross Origin Resource Sharing | A5 | CWE-942 |
| 299 | Client Side Testing | Testing for Cross Site Flashing | A3 | CWE-79 |
| 300 | Client Side Testing | Testing for Clickjacking | A5 | CWE-1021 |
| 301 | Client Side Testing | Testing WebSockets | A2 A3 | CWE-319 CWE-1347 |
| 302 | Client Side Testing | Testing WebSockets | A2 A3 | CWE-319 CWE-1347 |
| 303 | Client Side Testing | Testing Web Messaging | A5 | CWE-1020 |
| 304 | Client Side Testing | Testing Browser Storage | A1 A4 | CWE-312 CWE-313 CWE-315 CWE-922 |
| 305 | Client Side Testing | Testing for Cross Site Script Inclusion | A3 | CWE-79 |
| 306 | Client Side Testing | Testing for Cross Site Script Inclusion | A3 | CWE-79 |
| 307 | Client Side Testing | Testing for Client Side Script Include | A5 | CWE-79 |
| 308 | API Testing | Testing GraphQL | A3 | CWE-1347 |
| 309 | API Testing | Testing GraphQL | A3 | CWE-1347 |
| 310 | API Testing | Testing GraphQL | A3 | CWE-1347 |
| 311 | API Testing | Testing REST APIs | CWE-200 | |
| 312 | API Testing | Testing REST APIs | ||
| 313 | API Testing | Testing REST APIs | ||
| 314 | API Testing | Testing REST APIs | ||
| 315 | API Testing | Testing REST APIs | ||
| 316 | API Testing | Testing REST APIs | ||
| 317 | API Testing | Testing REST APIs | ||
| 318 | API Testing | Testing REST APIs | ||
| 319 | API Testing | Testing REST APIs | ||
| 320 | API Testing | Testing REST APIs | ||
| 321 | API Testing | Testing REST APIs | ||
| 322 | API Testing | Testing SOAP APIs | ||
| 323 | API Testing | Testing SOAP APIs | ||
| 324 | API Testing | Testing SOAP APIs | ||
| 325 | API Testing | Testing SOAP APIs | ||
| 326 | API Testing | Testing SOAP APIs | ||
| 327 | API Testing | Testing SOAP APIs | ||
| 328 | API Testing | Testing SOAP APIs | ||
| 329 | API Testing | Testing SOAP APIs | ||
| 330 | API Testing | Testing SOAP APIs | ||
| 331 | API Testing | Testing SOAP APIs | ||
| 332 | API Testing | Testing SOAP APIs | ||
| 333 | CMS | WordPress | A1 A4 | CWE-200 |
| 334 | CMS | WordPress | A5 | |
| 335 | CMS | WordPress | A6 | CWE-200 |
| 336 | CMS | WordPress | A1 A4 | CWE-264 |
| 337 | CMS | WordPress | A1 A4 | CWE-204 |
| 338 | CMS | WordPress | A1 A4 | CWE-200 |
| 339 | CMS | WordPress | A1 A4 | CWE-200 |
| 340 | CMS | WordPress | A1 A4 | CWE-548 |
| 341 | CMS | WordPress | A1 A4 | |
Trust us for:
- Installation Support
- Timely Renewal
- Zero-Day Trust
- Learning Something New
Do you have a complete oversight of your Security Posture?
Unlock Insights by Scheduling Your Comprehensive Discovery Call Now