RTaaS

Red Teaming as a Service
Real-World attacks, Real Protection.
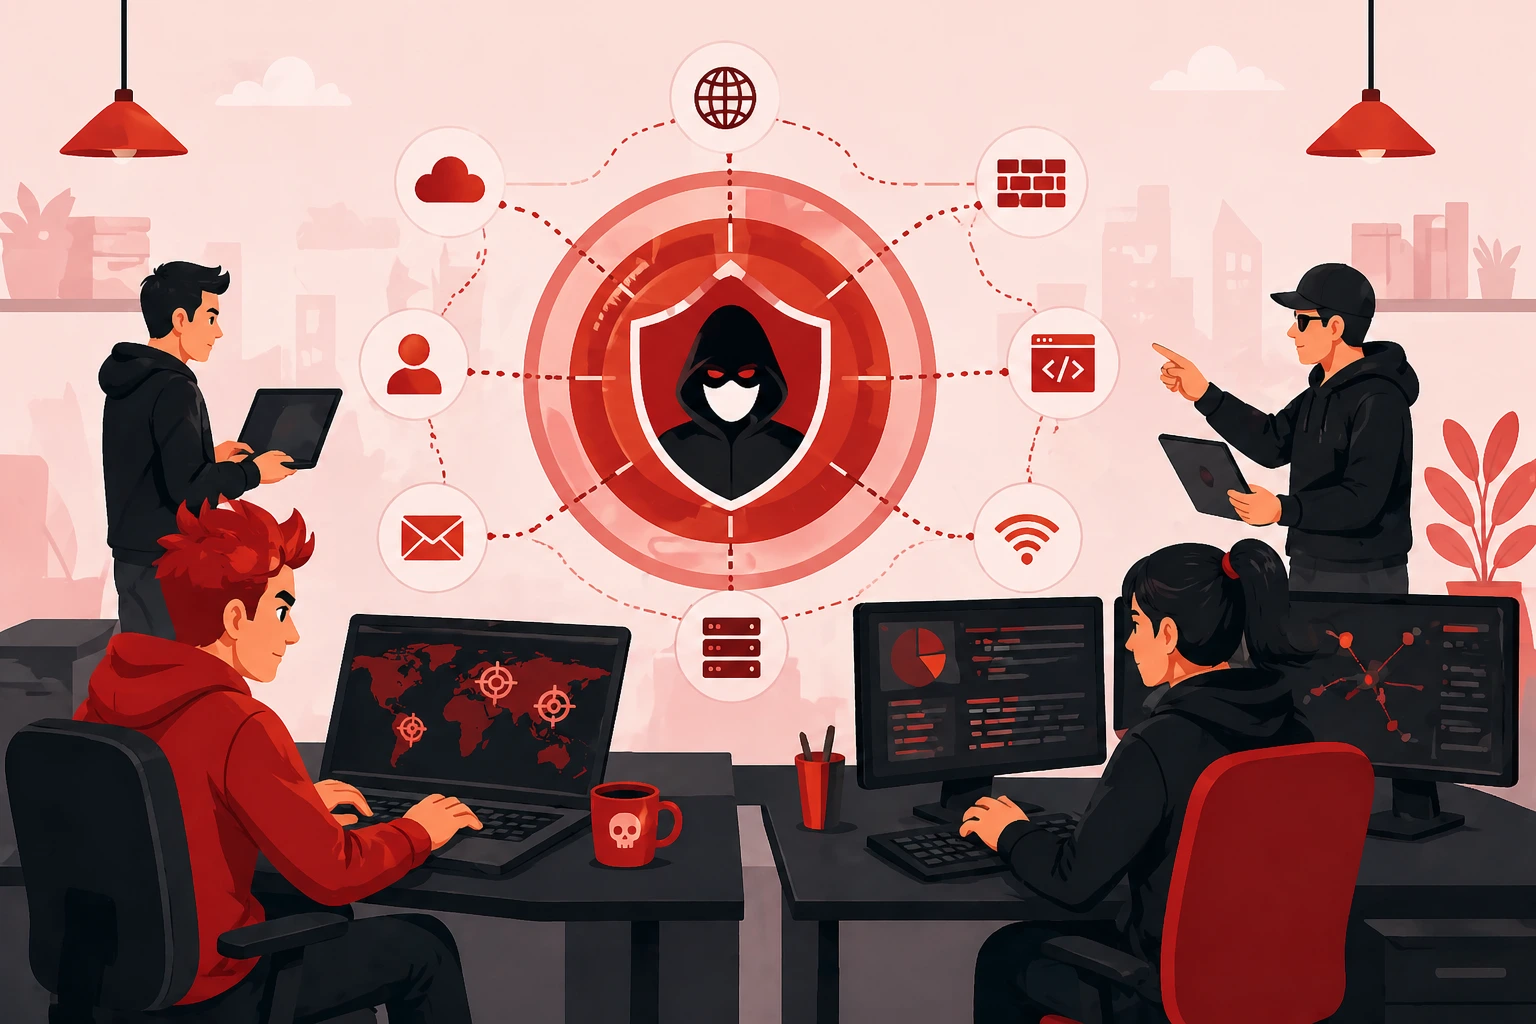
The most advanced test of your real-world security posture

RTaaS goes beyond vulnerability scanning and penetration testing. It simulates a full, sophisticated adversary campaign against your organisation — your technology, your people, and your processes — exactly the way a real threat actor would attack you.

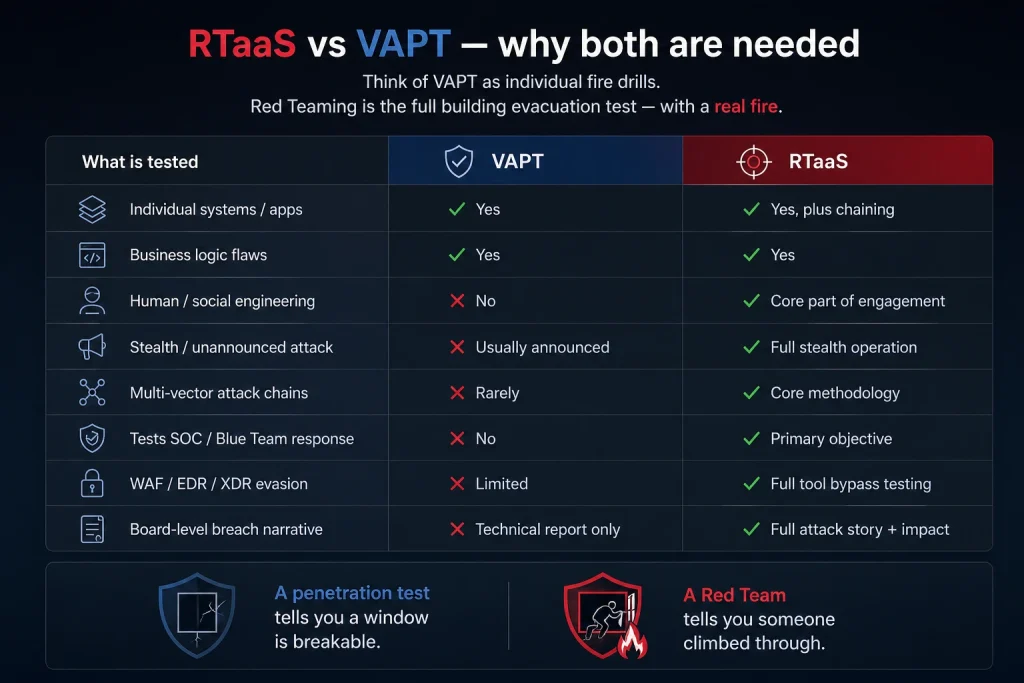
Most organisations believe they are secure because they run VA scans and annual Pentest. But here is the truth — VAPT tells you if the door can be broken. Red Teaming tells you if someone can walk into your building undetected, steal the keys from your own staff, disable your alarms, and leave without a single alert firing. RTaaS from Access0day is a full adversary simulation — not a checklist, not a scanner report — designed to expose exactly how a determined, skilled attacker would breach your organisation and what damage they could cause before your team even notices.

What Red Teaming actually tests — beyond VAPT
Infrastructure Hardening

Your People

Phishing, vishing, spear-phishing, and pretexting attacks test whether your staff are your strongest layer — or your biggest vulnerability.
os hardening


Physical security

Tailgating, impersonation, and physical intrusion simulation — testing if an attacker can walk in through your front door.
database hardening

Technology layers

Network, apps, Active Directory, cloud — but tested as an attacker moves through them, not as isolated systems.
network hardening

Detection & response

Does your SOC, SIEM, EDR, or XDR actually catch a real attacker? Red Teaming is the only way to find out before a real breach does.
firewall hardening

Lateral movement

Once inside, how far can an attacker move? Red Teams map the full blast radius — from initial access to domain compromise.
application hardening

Dwell time simulation

Real attackers stay hidden for weeks. Red Team operates in stealth — measuring how long before your team detects an intruder.

Certified Expertise You Can Trust

Every Access0day expert is certified by globally recognised security bodies — bringing validated, proven expertise to every engagement.
Secure Digital Technology to Enable Scalable Business Growth
Think your defences are strong? Prove it.

Red Teaming goes beyond scanning and testing individual systems. Our certified adversary simulation experts attack your entire organisation — your people, your processes, and your technology — exactly the way a real threat actor would. Stealth. Persistence. Precision. If there’s a way in, we’ll find it before someone else does.

The Question Every CIO and CISO Must Answer Before a Breach Forces it

If an attacker targeted your organisation today — not with an automated script, but with deliberate intent and real skill — how far would they get before anyone noticed?

Most security programs measure controls, coverage, and compliance.
Very few measure real-world resilience under attack. Access0day’s Red Team is designed to close that gap. We simulate advanced, targeted adversaries — not just to identify weaknesses, but to understand how those weaknesses translate into real business impact. Our approach mirrors real threat actors: patient, adaptive, and focused on achieving objectives.

  • Can critical systems be reached?
  • Can access be escalated and sustained?
  • Will your detection and response teams act in time?

The outcome is not a list of findings, but a clear, leadership-level view of risk — showing how close your organisation is to disruption, data exposure, or operational impact.

Because at the executive level, the real question is not “Are we secure?”
It is: “Are we prepared for a real attack?”
Simulating Real-World Attacks to Reveal Your True Security Posture
Active Directory Attack Chain — Kerberoasting, DCSync, BloodHound AnalysisActive Directory is the backbone of most enterprise environments — and the most targeted asset in advanced attacks. Our Red Team executes full AD attack chains including Kerberoasting, Pass-the-Hash, DCSync, and BloodHound-mapped privilege paths. If your AD is compromised, your entire organisation is compromised — we find out before an attacker does.
Full Red Team Engagement — Scoped to Your Environment and Threat ProfileEvery organisation faces a unique threat landscape. Our Red Team engagement is custom-designed around your industry, infrastructure, crown-jewel assets, and most likely adversaries. You don’t get a generic test — you get a simulation built around how a real attacker would specifically target your business.
MITRE ATT&CK Aligned — Every Attack Mapped to Real Adversary TTPsThe MITRE ATT&CK framework is the global standard for documenting how real-world threat actors operate. Every technique our Red Team uses is mapped directly to known adversary tactics, techniques, and procedures. This means your findings aren’t abstract — they reflect exactly how actual APT groups and cybercriminal organisations would attack you.
Lateral Movement + Privilege Escalation Across Your Internal EnvironmentGetting inside is only the beginning. Once initial access is gained, our Red Team moves through your environment exactly as a real attacker would — escalating privileges, accessing sensitive systems, and expanding their foothold deeper into your infrastructure. This reveals how far a real breach could go and which internal controls are actually stopping an attacker versus which ones are just assumed to work.
WAF / EDR / XDR Evasion — Testing If Your Tools Catch a Real AttackerSecurity tools are only as effective as their configuration and tuning. Our Red Team uses advanced evasion techniques to test whether your WAF, EDR, and XDR solutions detect and block a sophisticated attacker — or whether they can be bypassed silently. Most organisations are shocked to discover how long a skilled attacker can operate undetected inside a tool-protected environment.
C2 (Command & Control) Infrastructure SimulationReal attackers maintain persistent, covert communication channels inside compromised environments — sometimes for months. Our Red Team deploys realistic Command and Control infrastructure to simulate this behaviour, testing whether your network monitoring, SIEM, and security team can detect and disrupt an attacker who has already established a foothold. If your C2 detection fails, an attacker owns your environment indefinitely.
Real-Time Findings Dashboard — Live Visibility During the EngagementYou don’t have to wait until the end of the engagement to know what’s happening. Our live findings dashboard gives your security leadership real-time visibility into discovered vulnerabilities, attack progress, and risk-rated findings as they emerge. This means your team can begin prioritising responses immediately — not weeks after the test concludes.
Full Red Team Report — Executive Narrative + Technical Deep-DiveYour Red Team report speaks two languages simultaneously. The executive narrative translates the attack story into clear business impact — what was at risk, what was accessed, and what it would have cost in a real breach. The technical deep-dive gives your security team every detail they need to understand, reproduce, and remediate each finding with precision.
Free Retest Within 30 Days — Verify Your Remediations ActuallyFixing a vulnerability and confirming it is fixed are two very different things. Within 30 days of your engagement, our team retests every critical finding to verify that your remediation actually closes the attack path — not just on paper, but against the same techniques we used the first time. You walk away with confirmed closure, not just a to-do list.

Blue Team Debrief — Detailed Walkthrough of Every Detection GapYour defensive team learns as much from a Red Team engagement as your leadership does. Our Blue Team debrief walks your SOC, IR, and security operations staff through every step of the attack — what fired, what didn’t, where detection failed, and how your monitoring and response capabilities can be measurably improved. This turns a security test into a training opportunity for your entire defensive operation.
Compliance Support — CERT-In, RBI, SEBI, ISO 27001, PCI-DSS AlignedRegulatory requirements for security testing are tightening across every industry in India and globally. Our Red Team engagements are structured to satisfy the penetration testing and adversary simulation requirements of CERT-In, RBI, SEBI, ISO 27001, and PCI-DSS frameworks. Your report is written to be audit-ready — giving you evidence of due diligence that holds up to regulatory scrutiny.
Dedicated Red Team Consultant + Email & Virtual SupportFrom scoping call to final debrief, you have a single dedicated consultant who understands your environment, your concerns, and your business context. Our team is reachable throughout the engagement — no ticket queues, no account managers passing messages. Direct access to the expert doing the work, not just reporting on it.
Phishing + Spear-Phishing Campaigns with AI-Crafted, Context-Aware LuresGeneric phishing emails no longer fool anyone — but targeted, personalised ones still do. Our Red Team uses AI-assisted intelligence to craft highly convincing spear-phishing campaigns tailored to your organisation, your employees’ roles, and your business context. This tests your human layer the way real attackers do — not with obvious fake emails, but with ones your staff genuinely might click.
PTaaS vs. RTaaS What Matters to the Business

Red Teaming is not for every stage — but if you’re ready, it changes everything.

Every RTaaS engagement is custom-scoped. Talk to our Experts — no jargon, no obligation, just a clear conversation about your environment and what a Red Team would uncover.

Red Team engagements are scoped individually. Connect with us and our Expert will design a simulation tailored to your environment and threat profile. Learn More ……

Talk to us Unparalleled ExpertiseCutting-Edge TechniquesTailored SolutionsProactive ApproachTrusted Partnership

Work with a team that understands real-world threats and focuses on what truly matters to your business.
Gain clarity, reduce risk, and strengthen your security with confidence.

Do you have a complete oversight of your Security Posture?

Unlock Insights by Scheduling Your Comprehensive Discovery Call Now